What is the CIA Triad?
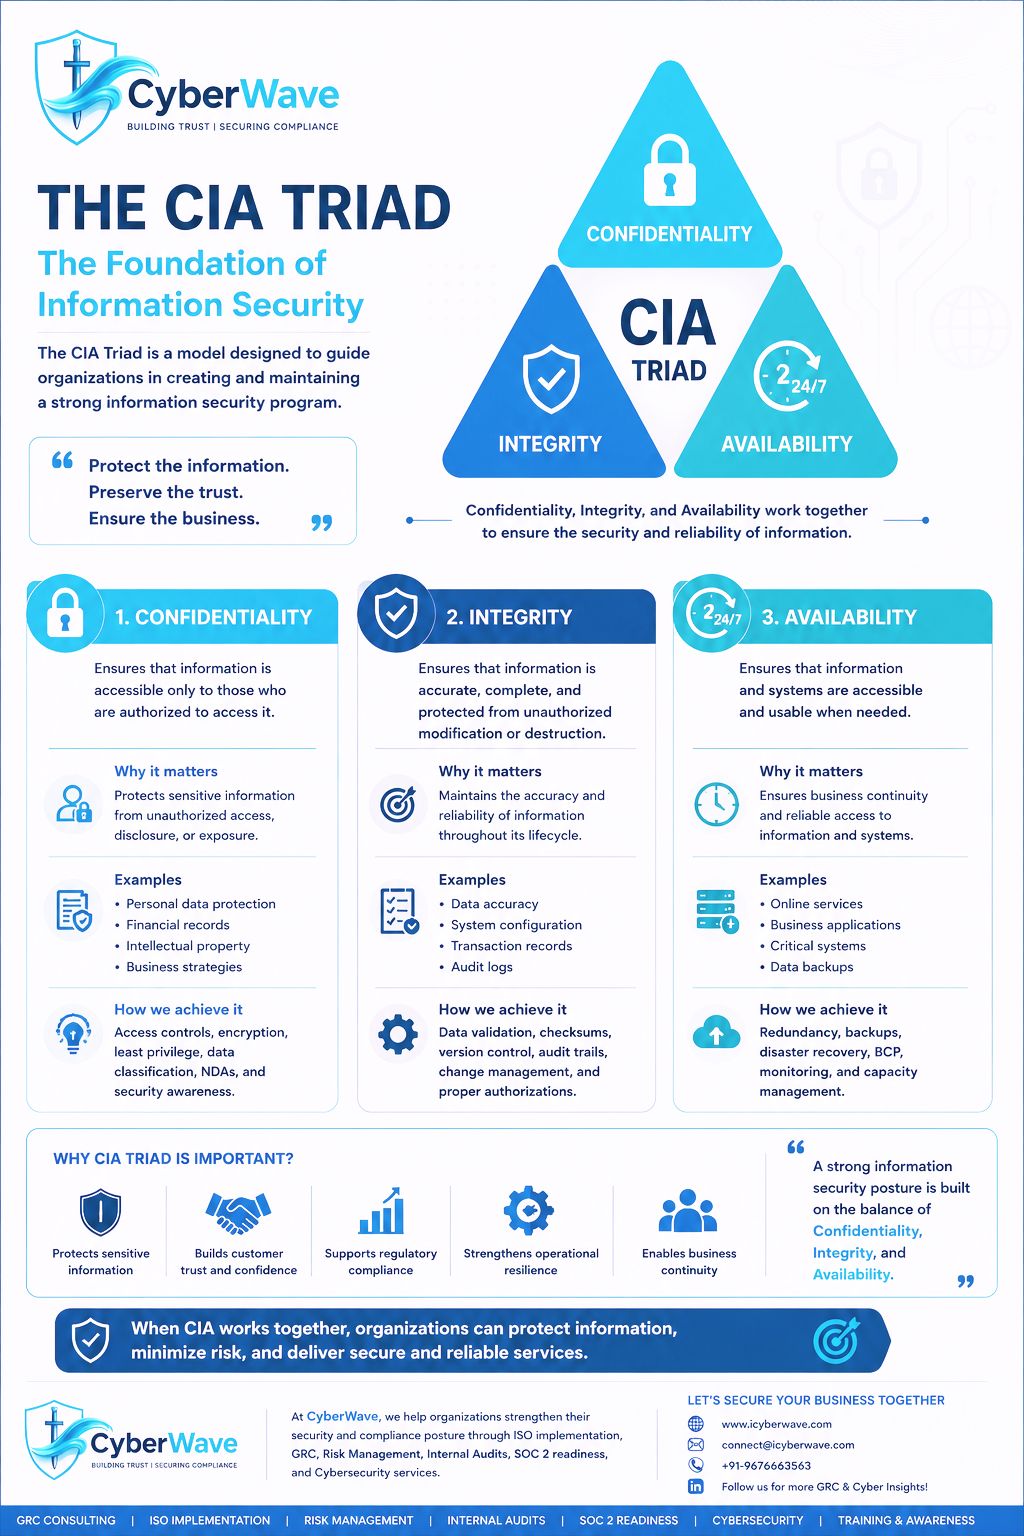
The CIA Triad is the model that guides organisations in building and maintaining a strong information security programme. Every security control, policy and audit ultimately exists to protect one or more of these three properties. When auditors assess your controls — whether for ISO 27001, SOC 2 or an internal review — they are asking: does this protect confidentiality, integrity, or availability?
Protect the information. Preserve the trust. Ensure the business.
1. Confidentiality
Definition: information is accessible only to those authorised to access it.
Why it matters: it protects sensitive information from unauthorised access, disclosure or exposure — the breaches that make headlines and trigger regulatory penalties.
- Examples of what it protects:
- Personal data and customer records
- Financial records
- Intellectual property
- Business strategies
How you achieve it: access controls, encryption, least privilege, data classification, NDAs and security awareness training.
2. Integrity
Definition: information is accurate, complete and protected from unauthorised modification or destruction.
Why it matters: integrity maintains the accuracy and reliability of information throughout its lifecycle. Decisions made on corrupted data are worse than decisions made on no data.
- Examples of what it protects:
- Data accuracy in databases
- System configuration
- Transaction records
- Audit logs
How you achieve it: data validation, checksums, version control, audit trails, change management and proper authorisations.
3. Availability
Definition: information and systems are accessible and usable when needed.
Why it matters: availability ensures business continuity — reliable access to the information and systems the business runs on. A perfectly confidential system nobody can reach is a failed system.
- Examples of what it protects:
- Online services
- Business applications
- Critical systems
- Data backups
How you achieve it: redundancy, backups, disaster recovery, business continuity planning, monitoring and capacity management.
Why the triad matters in practice
- Protects sensitive information across its entire lifecycle
- Builds customer trust and confidence — demonstrably, through audits and certifications
- Supports regulatory compliance — DPDP Act, GDPR, ISO 27001 and SOC 2 all map back to these three properties
- Strengthens operational resilience and enables business continuity
When the three pillars work together, organisations can protect information, minimise risk and deliver secure, reliable services. A strong security posture is built on the *balance* of confidentiality, integrity and availability — over-rotating on one at the expense of the others is itself a risk.
Where to go next
See how these principles become auditable controls in our ISO 27001 audit checklist and SOC 2 compliance checklist, explore our ISO 27001 consulting and SOC 2 services, or learn how security fits with governance in Cybersecurity vs GRC.