Different lenses, shared goal
Cybersecurity and GRC (Governance, Risk and Compliance) are often used interchangeably — and that confusion leaves gaps. They are different disciplines with different owners, tools and outputs, but one shared goal: a secure and compliant organisation.
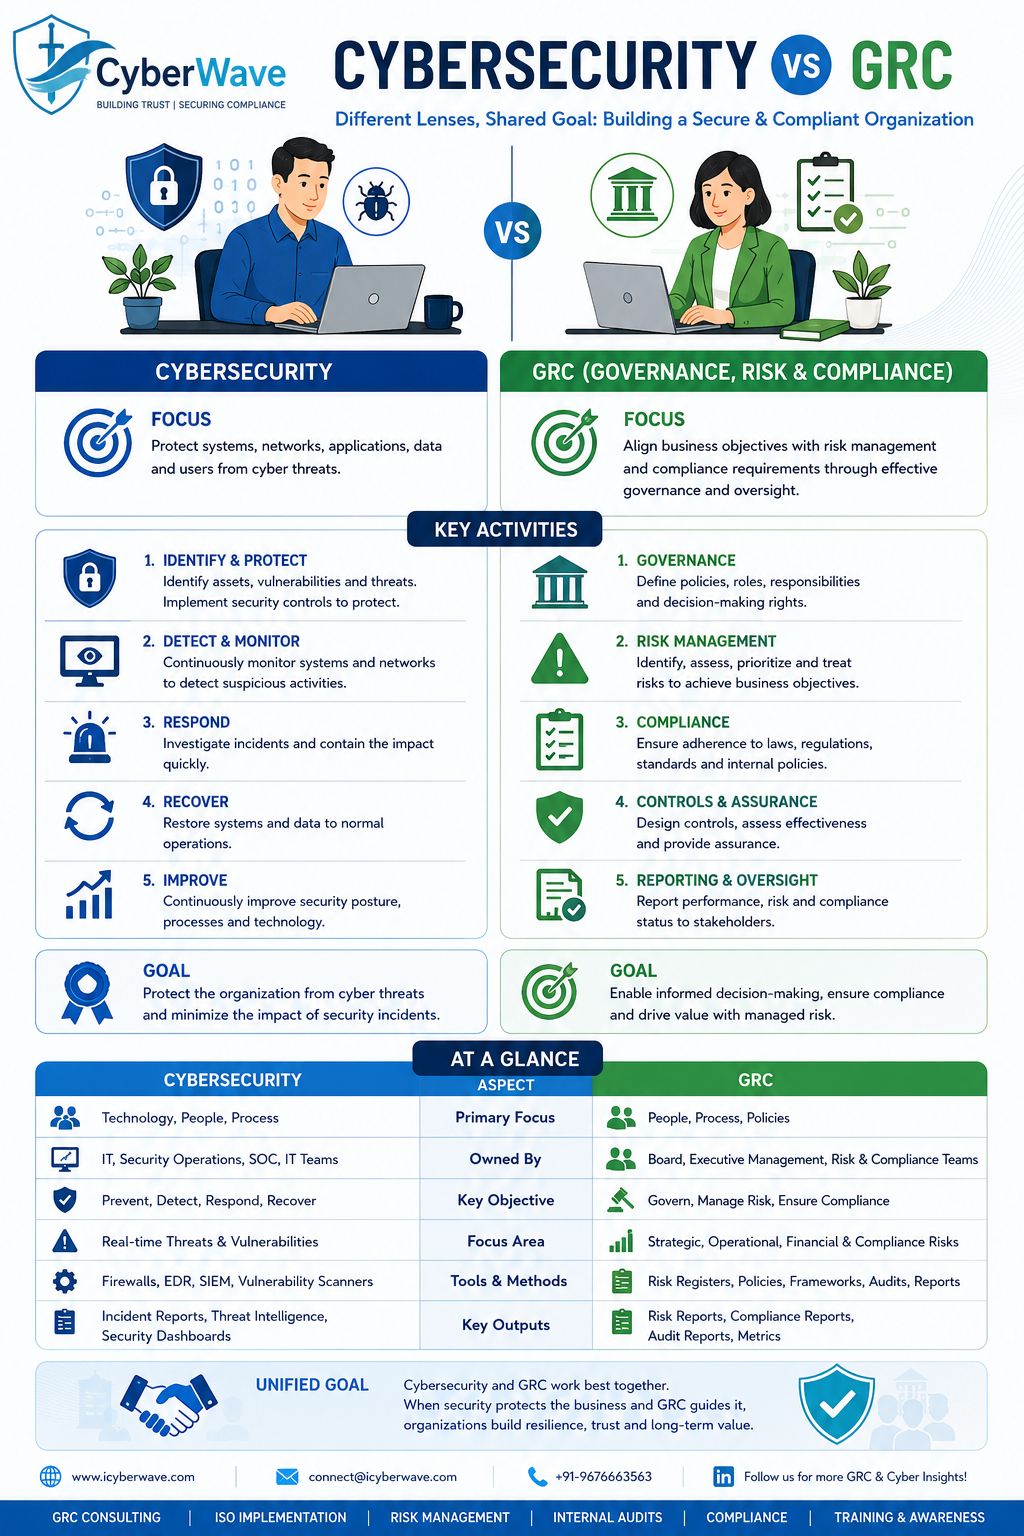
Cybersecurity: protect the technology
Focus: protect systems, networks, applications, data and users from cyber threats.
- Key activities:
- Identify and protect — identify assets, vulnerabilities and threats; implement security controls
- Detect and monitor — continuously monitor systems and networks for suspicious activity
- Respond — investigate incidents and contain the impact quickly
- Recover — restore systems and data to normal operations
- Improve — continuously improve the security posture, processes and technology
Goal: protect the organisation from cyber threats and minimise the impact of security incidents.
GRC: align the business
Focus: align business objectives with risk management and compliance requirements through effective governance and oversight.
- Key activities:
- Governance — define policies, roles, responsibilities and decision-making rights
- Risk management — identify, assess, prioritise and treat risks to achieve business objectives
- Compliance — ensure adherence to laws, regulations, standards and internal policies
- Controls and assurance — design controls, assess effectiveness and provide assurance
- Reporting and oversight — report performance, risk and compliance status to stakeholders
Goal: enable informed decision-making, ensure compliance and drive value with managed risk.
At a glance
| Aspect | Cybersecurity | GRC |
|---|---|---|
| Primary focus | Technology, people, process | People, process, policies |
| Owned by | IT, Security Operations, SOC, IT teams | Board, executive management, risk and compliance teams |
| Key objective | Prevent, detect, respond, recover | Govern, manage risk, ensure compliance |
| Focus area | Real-time threats and vulnerabilities | Strategic, operational, financial and compliance risks |
| Tools and methods | Firewalls, EDR, SIEM, vulnerability scanners | Risk registers, policies, frameworks, audits, reports |
| Key outputs | Incident reports, threat intelligence, security dashboards | Risk reports, compliance reports, audit reports, metrics |
The unified goal
Cybersecurity and GRC work best together. When security protects the business and GRC guides it, organisations build resilience, trust and long-term value. Cybersecurity without GRC produces technically strong controls that nobody can prove to an auditor or a board. GRC without cybersecurity produces beautiful policies that stop no attacker.
In practice this is why frameworks connect the two: NIST CSF 2.0 added the Govern function precisely to join security operations to oversight, and certifications like ISO 27001 require both the technical controls and the management system around them. Understanding the risk owner vs control owner split is where the two disciplines meet day to day.
CyberWave GRC works on both sides — GRC consulting, ISO implementation, risk management, internal audits, SOC 2 readiness and cybersecurity services. Get in touch to discuss where your gaps are.