Ask around about getting ISO 27001 in four weeks and most people will tell you it can't be done. Six months minimum, they'll say. Probably a year.
For most organisations, they're right. But not for all. Here's how we helped a healthcare client go from kickoff to a successful certification audit in four weeks, and why we'd tell most companies not to try it.
The situation
Our client was a healthcare organisation with a large new project lined up. The customer behind that project made ISO 27001 certification a condition, and the start date wasn't moving. A normal six-month timeline would have meant losing the project.
They had one advantage: because they already handled sensitive health data, many basic security practices were in place. What they didn't have was an information security management system (ISMS): the documented scope, risk assessment, policies, records and management processes that ISO 27001 requires.
Why most people say four weeks is impossible
ISO 27001 isn't a checklist you tick off. Certification needs:
- A defined ISMS scope and a documented risk assessment and treatment plan.
- A Statement of Applicability covering the Annex A controls.
- Policies and procedures that match how the organisation actually works.
- Evidence that the ISMS is operating: records, an internal audit and a management review.
- Two certification audits by an accredited body: Stage 1 (documentation and readiness) and Stage 2 (implementation and effectiveness).
Each of those normally takes weeks on its own. Certification bodies are often booked months ahead.
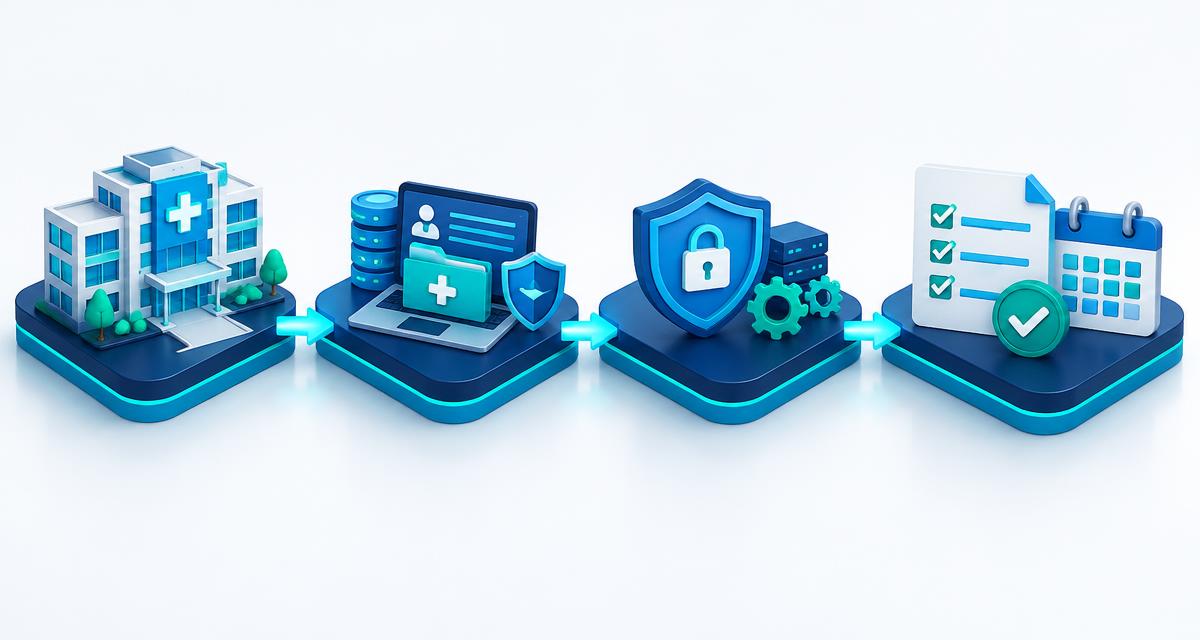
How we did it, week by week
Before day one: book the auditor. The first thing we did was secure Stage 1 and Stage 2 dates with the certification body. Without that, nothing else matters.
Week 1: scope, gaps and risks. We kept the scope tight around the services the new project needed. We ran a gap assessment against ISO 27001 clauses 4 to 10 and Annex A, completed the risk assessment with the client's leadership, and drafted the Statement of Applicability.
Week 2: policies and controls. Instead of writing from scratch, we started from our tested policy library and tailored every document to how the client actually operates. In parallel, the client's team closed the control gaps: access reviews, asset inventory, supplier reviews, logging and staff awareness training.
Week 3: make the ISMS run. We generated real records: access reviews, risk treatment decisions, incident and change logs. We ran an internal audit and a management review. Then came the Stage 1 audit.
Week 4: close and certify. We closed the Stage 1 observations within days and went into Stage 2. The audit ended with a recommendation for certification.
What made it possible
- A firm deadline and executive backing. Leadership cleared calendars and made decisions within hours, not weeks.
- A dedicated client team. The client assigned people full-time to the project for the four weeks.
- A tight scope. We certified what the business needed now, with a plan to expand later.
- A head start. Many controls already existed. We formalised, evidenced and filled gaps; we didn't build from zero.
- Experience. Our team has done this many times, so we knew what the auditor would ask for before they asked.
- Auditor dates secured first. The certification body's calendar is the real bottleneck.
What we didn't compromise on
Fast doesn't mean fake. Every policy was tailored, every record was real, and the internal audit and management review actually happened. Certification auditors are trained to spot a paper ISMS, and a certificate built on one won't survive the first surveillance audit.
When four weeks is not realistic
Be honest with yourself. Four weeks is unlikely if:
- You're starting with few or no security controls in place.
- Nobody on your side can give the project serious time.
- Your scope covers many sites, products or business units.
- You can't get certification audit dates soon.
- Leadership can't make decisions quickly.
For most organisations, 3 to 6 months is a realistic and much less stressful target. See our ISO 27001 certification cost in India guide for typical costs, and our ISO 27001 audit checklist for what auditors look for.