
Blog & Insights
Expert perspectives on cybersecurity, compliance, and risk management from the CyberWave GRC team.
ISO 22301 BCMS Implementation Roadmap: 13 Steps to Certification
A step-by-step ISO 22301:2019 implementation roadmap — from top management commitment and Business Impact Analysis to recovery objectives, exercising, internal audit and certification.
Cybersecurity vs GRC: What Is the Difference and Why You Need Both
Cybersecurity protects systems from threats; GRC aligns the business with risk and compliance obligations. Different lenses, shared goal — here is how the two disciplines differ and work together.
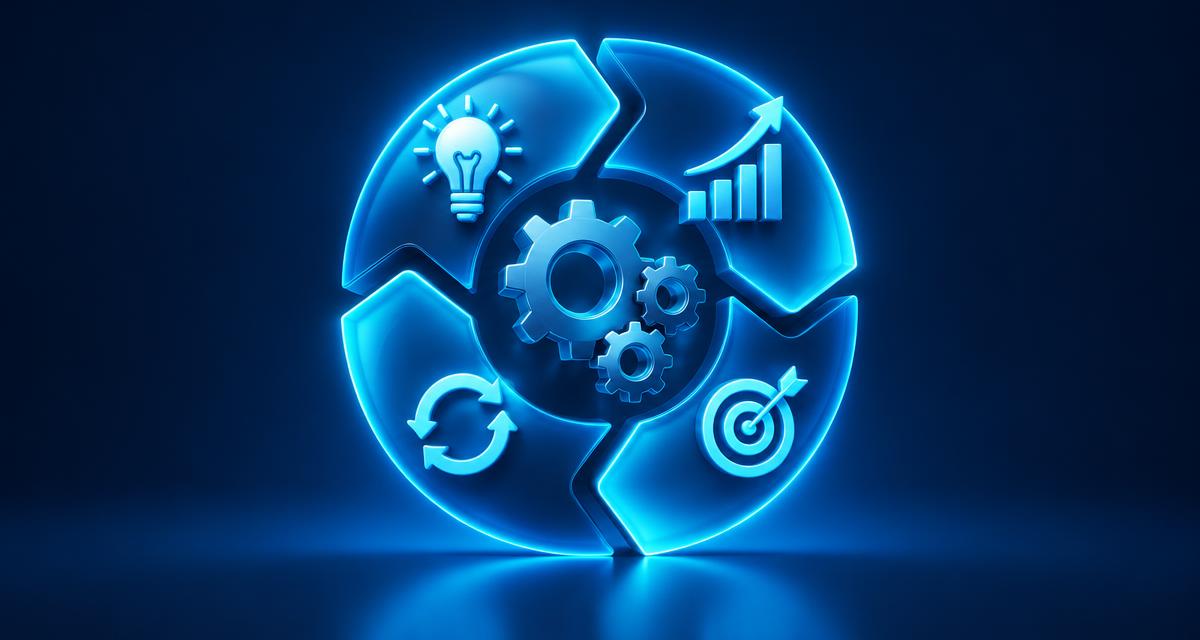
The PDCA Cycle Explained: Plan-Do-Check-Act for Continuous Improvement
The PDCA cycle is the engine inside every ISO management system. What each phase means, how ISO 27001, ISO 22301, ISO 9001 and ISO 20000 apply it, and why improvement never ends.
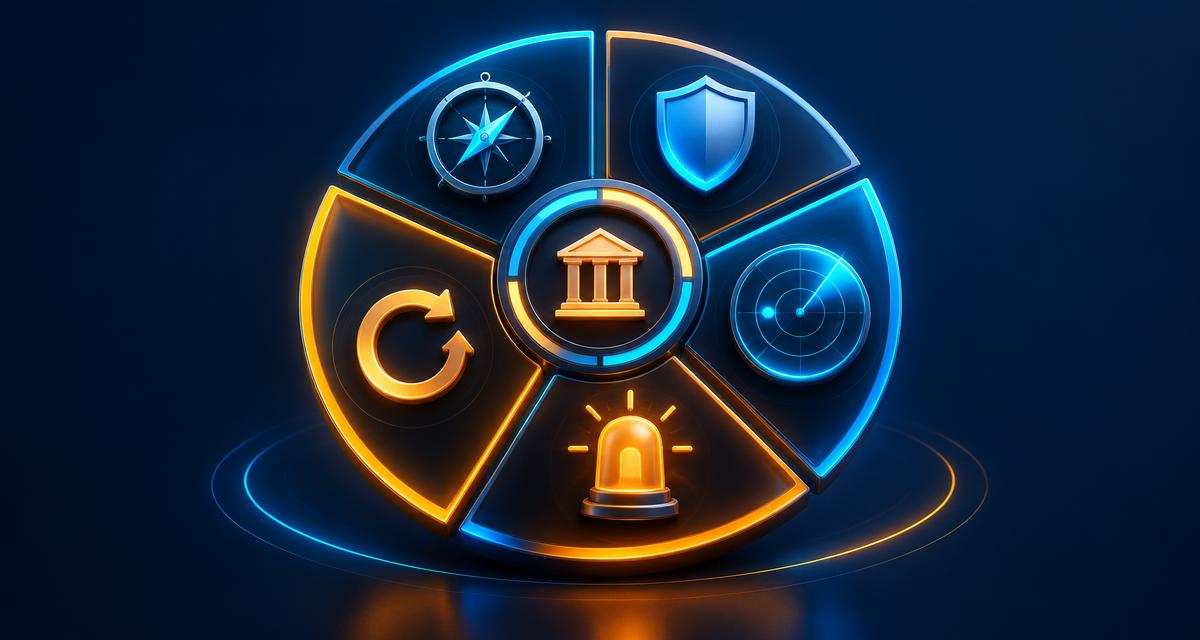
NIST CSF 2.0 Explained: The Six Functions and How to Use Them
NIST CSF 2.0 is the practical framework for managing cybersecurity risk. What it is, the six core functions including the new Govern function, who should use it, and how it compares to ISO 27001.
Risk Owner vs Control Owner: Roles, Responsibilities and Examples
Risk owners own the risk; control owners own the controls. The difference between the two roles, who reports to whom, decision authority, success measures and a practical example.
SOC 2 Compliance Checklist: Every Control, Evidence Item and Audit Step
A complete, auditor-tested SOC 2 compliance checklist — scoping decisions, all five Trust Services Criteria, the evidence auditors actually request, observation-window rules, common exceptions and a realistic 90-day readiness plan.
ISO 27001 Audit Checklist: Clause-by-Clause and Annex A Control Evidence
The ISO 27001:2022 audit checklist auditors work from — mandatory documented information, clauses 4 to 10, all 93 Annex A controls grouped by theme, the evidence that satisfies each, and the findings that most often delay certification.
ISO 42001 Certification: Requirements, Cost, Timeline and Step-by-Step Process
A practical guide to getting ISO/IEC 42001 certified — clause-by-clause requirements, Annex A controls, audit stages, realistic timelines and cost drivers, plus how AIMS maps to ISO 27001 and the EU AI Act.
Data Fiduciary Under India's DPDP Act: Duties, Liabilities and Compliance Checklist
Who counts as a Data Fiduciary under the DPDP Act, what obligations attach to that role, and how Significant Data Fiduciaries carry extra duties — explained with a practical compliance checklist.
DPDP Rules: How the Draft Rules Change Day-to-Day Compliance
The DPDP Act set the principles; the Rules set the mechanics. Here's how notice, consent managers, breach reporting timelines, retention periods and verifiable parental consent translate into operational work.
Audit Working Papers: Standards, Structure and Review Best Practices
Working papers are the audit's evidence of work performed. This guide covers what belongs in a working paper, permanent versus current files, review discipline, retention and the most common documentation findings.
Data Protection Officer: Role, Responsibilities and When You Must Appoint One
When a DPO appointment is mandatory under GDPR and India's DPDP Act, what the role actually does, the independence and conflict-of-interest rules, and how to choose between an in-house and an outsourced DPO.